Approval Matrix: Who Can Sign Off on a Rough Cut or Final Delivery?
Approval Matrix: Who Can Sign Off on a Rough Cut or Final Delivery?

An approval matrix is a structured schedule of authority that maps decisions to the people who can approve them, the limits on their authority, and the escalation path when those limits are exceeded. It speeds approvals, cuts bottlenecks, and makes accountability auditable. Managers, finance teams, and project or creative leads use it to keep decisions moving without losing control over who signed off on what.
TL;DR:
- Define each decision by role, explicit authority ceiling, approval type, escalation trigger, and delegation rule; record the approver, date, and matrix version for audits.
- Set thresholds from actual cost and risk, using clear numeric upper bounds such as $0 to $10,000 rather than subjective labels like small purchases.
- Pilot one workflow with approvers, track cycle time and feedback, then adjust unrealistic limits before expanding; schedule recurring reviews as roles and budgets change.
- Move beyond spreadsheets when approvals span departments, delegation is frequent, or audit trails require email reconstruction; creative teams need signoffs tied to exact file versions.
Table of Contents
- What an approval matrix actually is
- Why organizations need an approval matrix
- Key components of an approval matrix
- Examples and templates across common workflows
- How to design and implement an approval matrix step by step
- Templates, tools, and when a spreadsheet stops working
- How we think about approval tracking for creative teams
- What implementing approval matrices actually teaches you
- Where Posthive fits once you have a matrix
- FAQ
- Sources
What an approval matrix actually is
An approval matrix is sometimes called a schedule of authority or an authorization matrix, and most teams build it as a grid: decision categories down the rows, roles or titles across the columns, and authority limits in each cell. A finance team might use it to show who can approve a $5,000 purchase order versus a $50,000 one; a creative team might use it to show who signs off on a rough cut versus a final delivery.
A few terms matter before you build one:
- Decision category: the type of action being approved, such as a purchase, a hire, or a content release.
- Role: the position with authority, not the individual, so the matrix survives staff turnover.
- Authority limit: the ceiling on what a role can approve alone, expressed as a dollar amount, a risk tier, or a scope boundary.
- Joint approval: a rule requiring two or more sign-offs for higher-risk or higher-cost decisions.
- Escalation rule: what happens when a decision exceeds a role’s limit, and who it goes to next.
Capturing delegation and version history inside the matrix matters because auditors and internal reviewers need to see not just who approved something, but who was authorized to at the time.
Why organizations need an approval matrix
Without a documented schedule of authority, approvals stall in inboxes, get duplicated across people who think they own the decision, or slip through without anyone qualified reviewing them. A matrix fixes the handoff problem: everyone knows who owns the next step, so decisions do not wait on the wrong desk.
The control case is just as strong. COSO’s Internal Control framework identifies approval and authorization procedures as control activities that organizations must select and develop to manage risk and provide documented evidence of who holds what authority. Treating authorization as a formal control activity, as COSO frames it, turns the matrix into both a daily operating tool and audit evidence at the same time. That documentation is what lets an auditor confirm segregation of duties rather than taking a team’s word for it.
A matrix also scales decision quality. A ten-person studio can run approvals informally, but once a team adds regions, clients, or departments, an undocumented process produces inconsistent calls on similar decisions. A matrix keeps the threshold for a $20,000 vendor contract the same whether the request comes from New York or from a satellite office, which is the point of having one at all.

Key components of an approval matrix
A matrix is only useful if every cell answers a specific question. Build it around these fields rather than a vague “who approves this” column.
- Decision categories, granular enough to separate real risk differences (a $500 software renewal is not the same decision as a $500,000 vendor contract) but not so fine that the matrix becomes unreadable.
- Roles, not named individuals, paired with explicit delegation rules for when the role holder is unavailable.
- Authority limits, written as numeric thresholds (dollar amounts, hour counts) or categorical limits (risk tier, content type) so there is no ambiguity about what “within budget” means.
- Approval type, noting whether a decision needs a single sign-off, joint approval, or sequential review.
- Escalation path, naming exactly who a decision goes to next and under what trigger.
- Audit metadata, including date, version, and the name of the approver at the time of the decision.
Numeric limits are easier to enforce than categorical ones, so where possible, convert a judgment call (“significant risk”) into a number or a defined tier.
Pro Tip: Write authority limits as ranges with a clear upper bound (“$0 to $10,000”) rather than open-ended language like “small purchases,” which different approvers will interpret differently.
Examples and templates across common workflows
Most teams recognize an approval matrix faster through examples than through definitions. Here is how the same structure applies across four common workflows:
- Procurement: a buyer initiates a purchase request, a department manager approves up to a set threshold, and finance countersigns anything above it, typically with a second signature required once a purchase crosses a materiality line.
- Project approvals: each milestone (kickoff, draft, final delivery) has a named sign-off role, often the project lead for interim milestones and a client stakeholder or account director for final delivery.
- HR and recruitment: a hiring manager proposes an offer, HR confirms it fits the salary band, and anything above the band requires a department head or finance sign-off before the offer goes out.
- Marketing and content: a creative lead approves the first review round, a brand or legal reviewer checks compliance, and the budget holder signs off before spend is committed, often across two or more review rounds before final release.
Production and creative teams face one added wrinkle: approvals often attach to a specific file version, not just a decision. A two-round creative approval workflow that separates an internal review from a client-facing round keeps version confusion from leaking into the matrix itself.
How to design and implement an approval matrix step by step
Building a matrix works best as a short project with a clear order of operations, not a one-sitting spreadsheet exercise.
- Map your processes first. List every recurring decision type (purchases, hires, content releases) and the trigger that starts each one.
- Set thresholds grounded in risk and cost, not round numbers picked for convenience. A $10,000 threshold should reflect what actually represents meaningful risk for your organization, not an arbitrary line.
- Assign roles, not names, and document who delegates to whom when a role holder is out.
- Choose where the matrix will live, whether that is a shared document or a workflow tool, and build in escalation and audit fields from the start.
- Pilot it on one workflow, collect feedback from the people actually approving things, and adjust thresholds that turn out to be unrealistic.
- Train the team and schedule a recurring review, since roles, budgets, and risk tolerance all shift over time.
Practitioner guidance on control activities reinforces why the early steps matter most: authorization procedures exist specifically to translate risk insight into operational guardrails, preventing unauthorized payments and conflicts of interest before they happen, rather than catching them after the fact.
| Step | Main output |
|---|---|
| Map processes | List of decision types and triggers |
| Set thresholds | Dollar or risk-tier limits per category |
| Assign roles | Role-to-authority mapping with delegation rules |
| Build and test | Matrix with escalation and audit fields |
| Pilot and review | Feedback loop and a review schedule |
Templates, tools, and when a spreadsheet stops working
Most teams start with a spreadsheet: categories in rows, roles in columns, limits in cells. It works until multiple approvers, frequent threshold changes, or media files enter the picture. Spreadsheets commonly fail for approval matrices because of manual edits that overwrite prior approvals, no real version control, and no way to enforce who is allowed to change a cell.
Watch for these signals that it is time to move to a dedicated tool:
- You have more than a handful of approvers across more than one department.
- You need an audit trail that shows exactly who approved what, and when, without reconstructing it from email threads.
- Delegation happens often enough that manual tracking creates gaps.
When you move off a spreadsheet, prioritize delegation with expiry dates, automated reminders, a permanent audit log, and role-based access so people only see and approve what their role covers. Creative teams specifically need review rounds, in-context annotations, and delivery receipts, since an approval often needs to point at a specific frame or file version rather than a line item. Media sharing permissions that control who can view or approve a given asset version are part of that same access-control picture.
Pro Tip: Before switching tools, pilot your matrix on one workflow for two weeks. If approvers still revert to email or chat to get a decision made, the tool needs tighter integration with where people already work, not more features.
How we think about approval tracking for creative teams
Creative approvals carry a complication most matrices ignore: the decision usually attaches to a specific asset version, not just a category and a dollar amount. A client approving “the final cut” needs that approval tied to the exact file, not a general sign-off that gets misapplied to a later revision.
A pilot worth running in a week:
- Map one real workflow (a single project’s review cycle) end to end.
- Assign roles and limits to each step, including who signs off on the final client-facing version.
- Run the pilot live and track where approvals stall.
- Review what broke and adjust before rolling it out further.
Our one-week approval tracking pilot and our deliverable sign-off checklist walk through this in more detail for project and creative leads.
What implementing approval matrices actually teaches you
The most common failure mode is not a missing matrix. It is a matrix built in isolation from the people who use it daily, so thresholds feel arbitrary and approvers route around it within a month. The fix is simple: pilot one workflow, measure how long approvals took before and after, and let that number decide whether the thresholds need adjusting before you expand to a second workflow.
Start smaller than feels productive. One workflow, one measured cycle time, one round of real feedback beats a fully built matrix that nobody actually follows.
— Lorenz
Where Posthive fits once you have a matrix
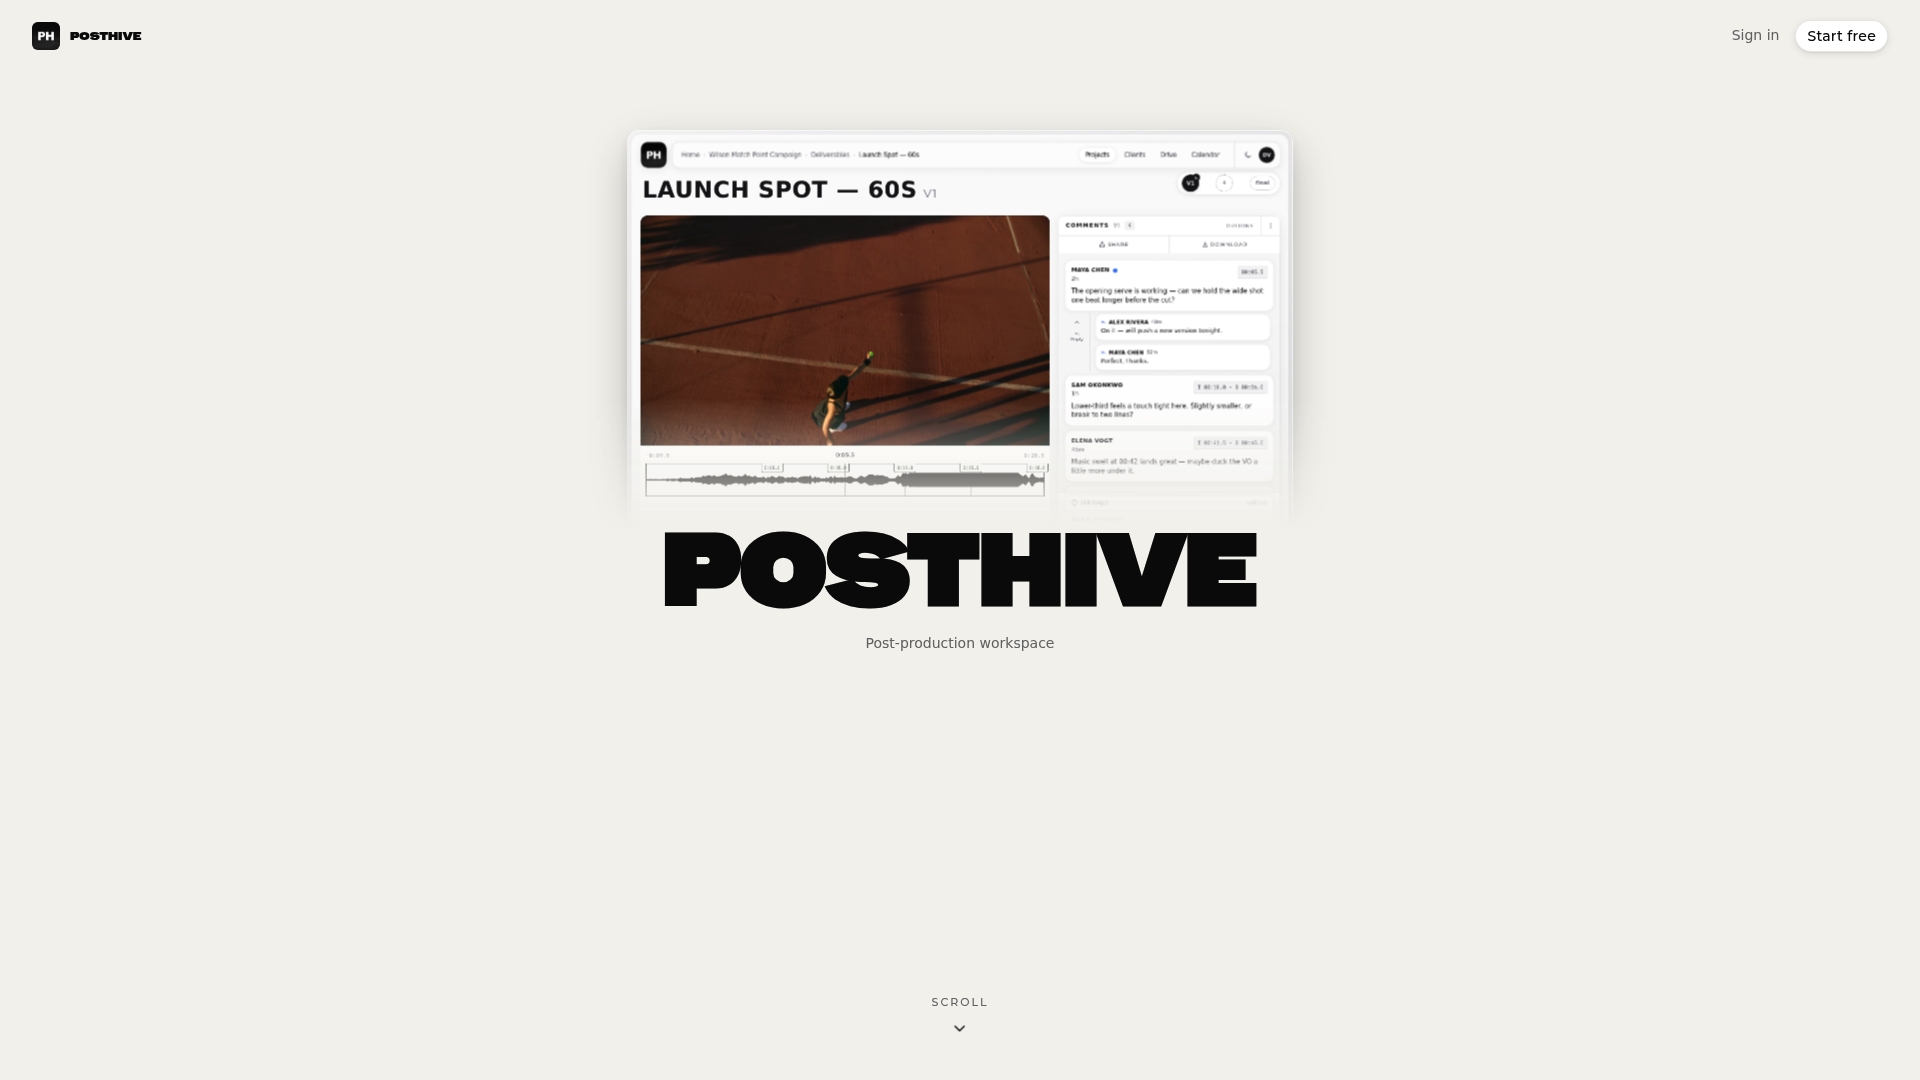
Once a matrix exists, the harder part is making it stick to actual files and versions, which is where most spreadsheets and email threads quietly fail. Our platform addresses that gap by keeping version history for every deliverable, maintaining client ownership of files and feedback, and attaching approval tracking to the exact asset being reviewed rather than a general sign-off that may misapply to later versions.
Every plan includes unlimited free seats, so clients and reviewers can take part in approval rounds without your team paying per added person. If you want to see how that works against a real project, our Pro and Enterprise plans start a pilot you can run this week, or you can look through what the platform covers first.
FAQ
What is the purpose of an approval matrix?
An approval matrix exists to assign clear authority for decisions and make accountability auditable, so approvals move faster and no one signs off outside their authorized limit. It also gives auditors documented evidence of who was authorized to approve what, which COSO’s control framework treats as a required control activity.
What is an authorization matrix?
An authorization matrix is another name for an approval matrix: a grid mapping decision types to the roles authorized to approve them and the limits on that authority. Some teams use the terms interchangeably, while others use “authorization matrix” specifically for financial sign-off limits.
What is the format of a decision matrix?
Most approval or decision matrices use a grid format, with decision categories listed as rows and roles or titles as columns, and each cell showing the authority limit or approval requirement for that combination. Some versions add extra columns for escalation paths and audit fields like approval date and version.
What is the approval hierarchy?
An approval hierarchy is the ordered chain of roles a decision moves through, starting with the role closest to the request and escalating upward when a decision exceeds that role’s authority limit. It is the escalation logic inside an approval matrix rather than a separate document.
Sources
- COSO Internal Control—Integrated Framework
- Step 3: COSO control activities drive the best governance